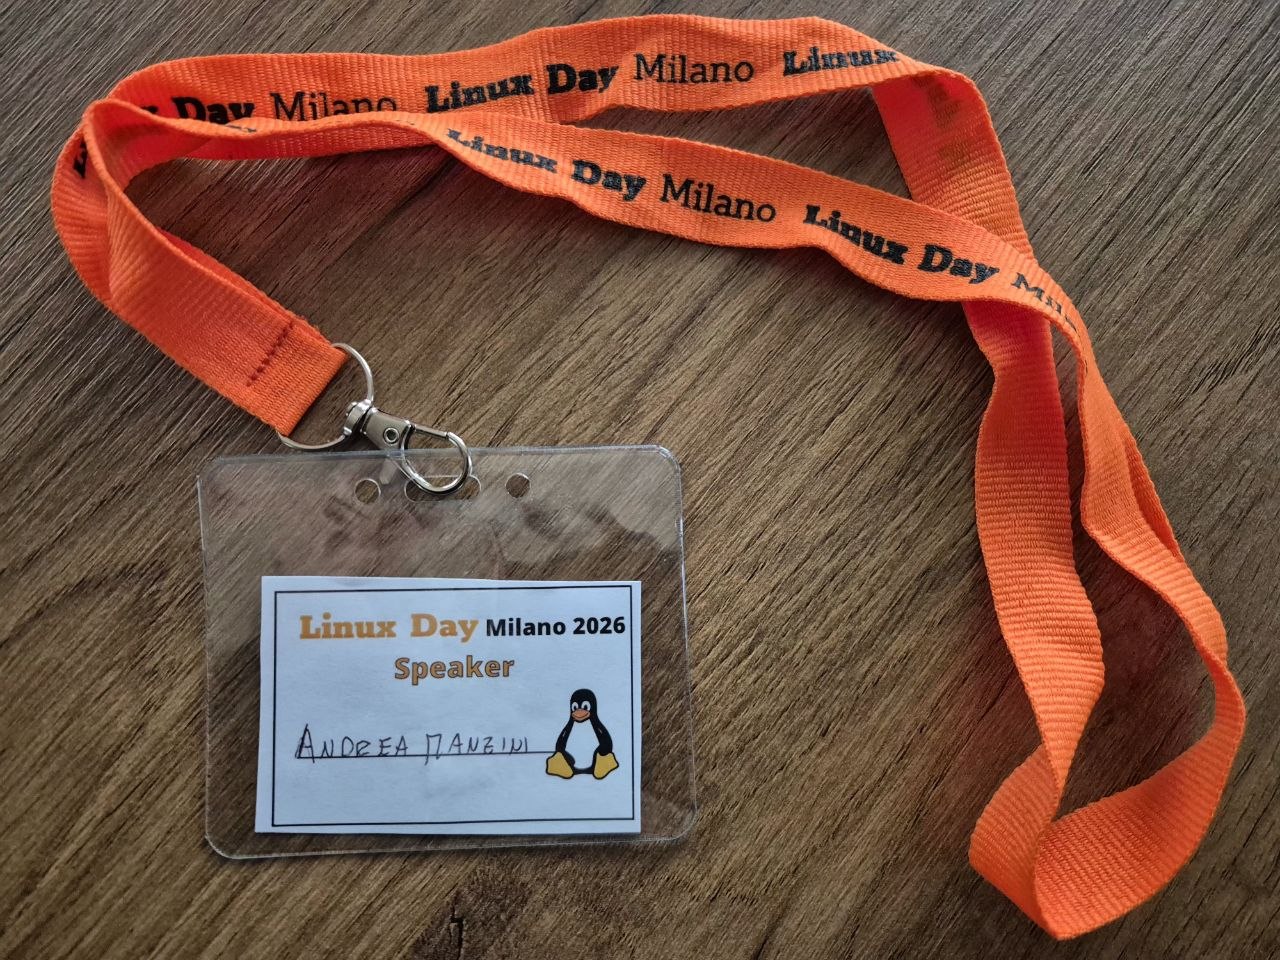
Linux Day Milano 2026 Badge

Linux Day Milano 2026 recap

Intro On Saturday, October 24th, 2026, I had the pleasure of attending Linux Day Milano 2026. For those unfamiliar with it, Linux Day is the premier nationwide event in Italy dedicated to GNU/Linux, Free Software, and open culture. Promoted annually since 2001 by the Italian Linux Society (ILS) on the fourth Saturday of October, it is held simultaneously across dozens of Italian cities thanks to local Linux User Groups (LUGs), student groups, and passionate volunteers. It remains the most important grassroots gathering for open source enthusiasts and professionals in the country. ...


November 2, 2026 · Andrea Manzini

How much code are you testing ? (5)

🧭 Where we left off Welcome back to our technical journey on measuring binary test coverage! In part 4 we introduced funkoverage, a native, high-performance eBPF-based coverage tracer that leverages uprobe_multi to capture function entry events in GNU/Linux with less than 2% overhead. It parses static library dependencies using ldd during installation and maps uprobes to all discovered functions. But there was a big fat elephant in the room: dlopen(). Some of the most complex, modular software in the world — such as web servers with dynamic modules, plugin-based enterprise applications, and multi-protocol databases — load their dependencies at runtime on-the-fly. Because these libraries are not declared in the ELF binary’s DT_NEEDED header, they are invisible to ldd during installation. Today, we are going to chase the dynamic loading ghost, explore how we solved this with an elegant, highly scalable, event-driven eBPF JIT instrumentation strategy, and battle-test it live on standard, unmodified production binaries like Nginx and OpenSSL! ...

August 11, 2026 · Andrea Manzini

How much code are you testing ? (4)

🧭 Where we left off Welcome back to our ongoing series on measuring test coverage for binary programs! In part 1 we used Go’s built-in -cover flag — clean and accurate, but only works if you own the source and can recompile. In part 2 we used valgrind and gdb to trace gzip without touching its source. In part 3 we explored Intel PIN, a proper dynamic binary instrumentation framework — powerful, but it came with a ~100MB proprietary C++ SDK and was limited to x86_64. ...

May 13, 2026 · Andrea Manzini

playing with eBPF interface - 2

In the last post we introduced the BCC framework to interface Python code with eBPF facility. Now we are ready to make one step further! #!/usr/bin/python3 import bcc bpf = bcc.BPF(text=""" #include <uapi/linux/ptrace.h> int trace_malloc(struct pt_regs *ctx, size_t size) { bpf_trace_printk("size=%d\\n",size); return 0; };""") bpf.attach_uprobe(name="c",sym="malloc",fn_name="trace_malloc") while 1: (task, pid, cpu, flags, ts, msg) = bpf.trace_fields() print(f"task={task}\tmsg={msg}") This code is a little more complex, but still quite easy: first of all we use bcc to attach an “user space probe” instead of a kernel probe, and the function being observed will be libc’s malloc. ...

May 19, 2021 · Andrea Manzini
Buy Me a Coffee at ko-fi.com Buy Me A Coffee

This site does not use cookies or collect any personal data. © 2026 Andrea Manzini.